Security

Azure Support Agent runs in the deployed environment and is designed around read-only defaults, explicit write approvals, tenant scoping, RBAC/SSO, encrypted credentials, and audit records. Security still depends on deployment configuration, provider contracts, Azure/Graph grants, and administrator choices.
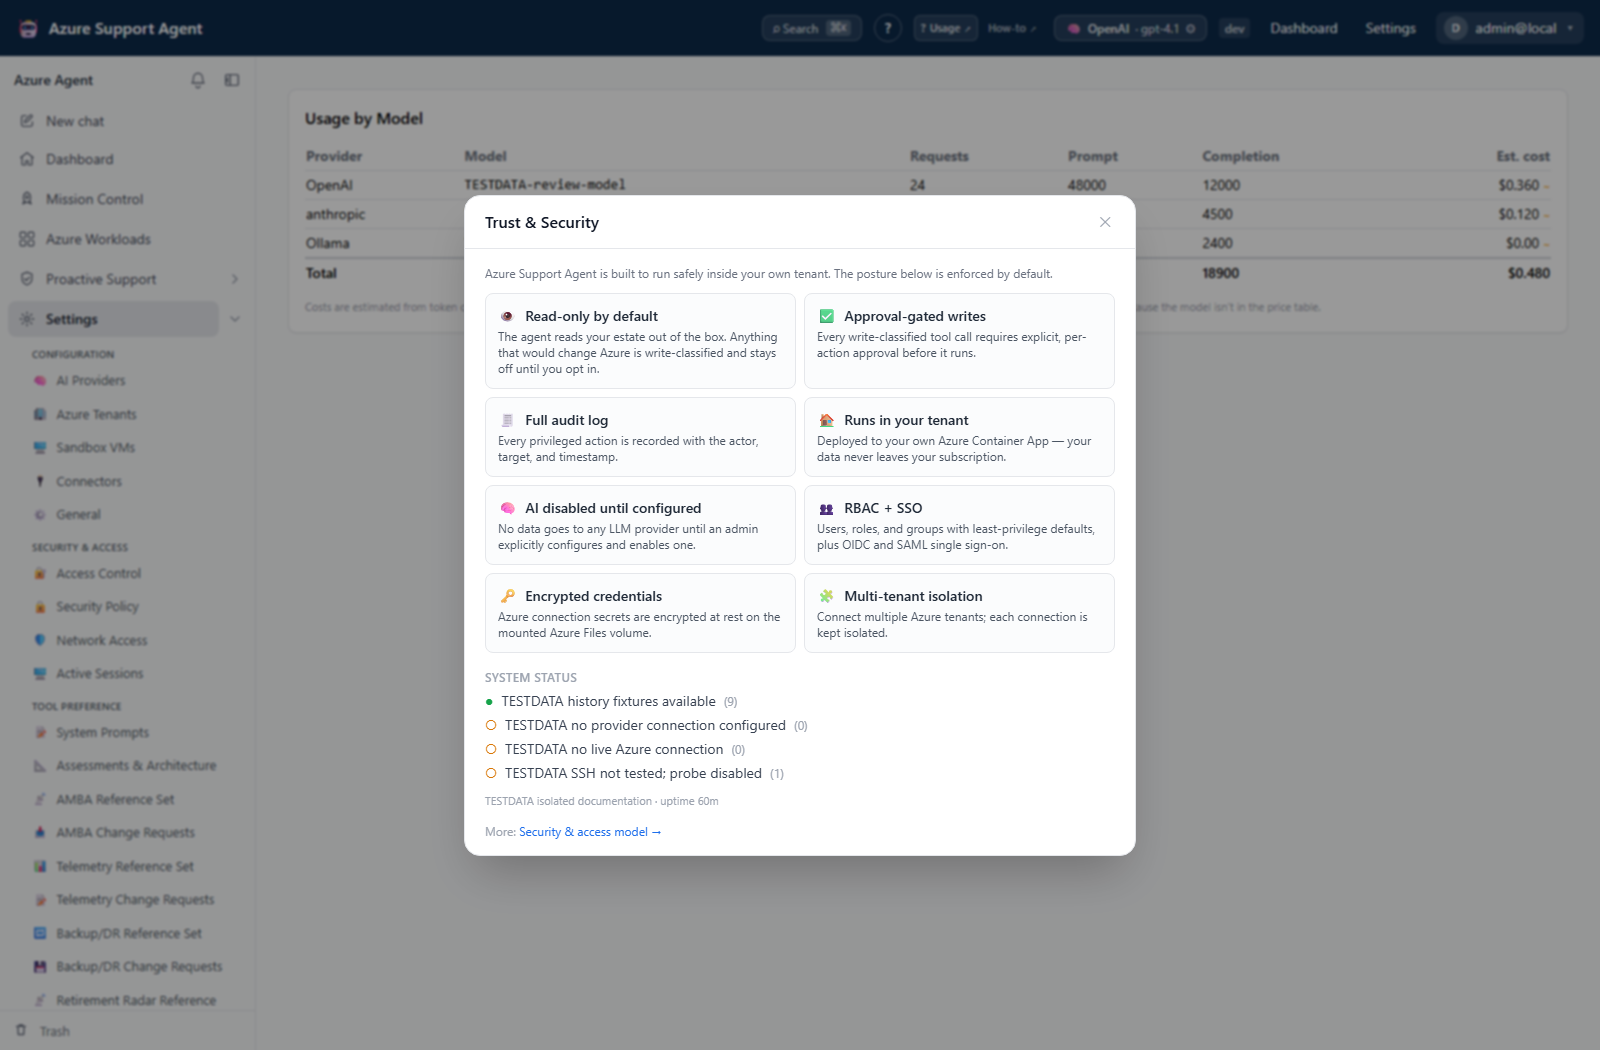
Help Trust & Security — guidance and illustrative status checks
Help Trust & Security — guidance and illustrative status checks. The native help dialog presents the shipped trust guidance beside dummy system-status checks, including no provider connection, no live Azure connection, and an untested disabled SSH host. The help copy is not independent certification; these examples do not verify encryption, egress, deployment location, tenant isolation, or successful probes. Background usage figures are also synthetic. Synthetic example data; names, identifiers and measurements do not describe a live tenant. View full-size screenshot.
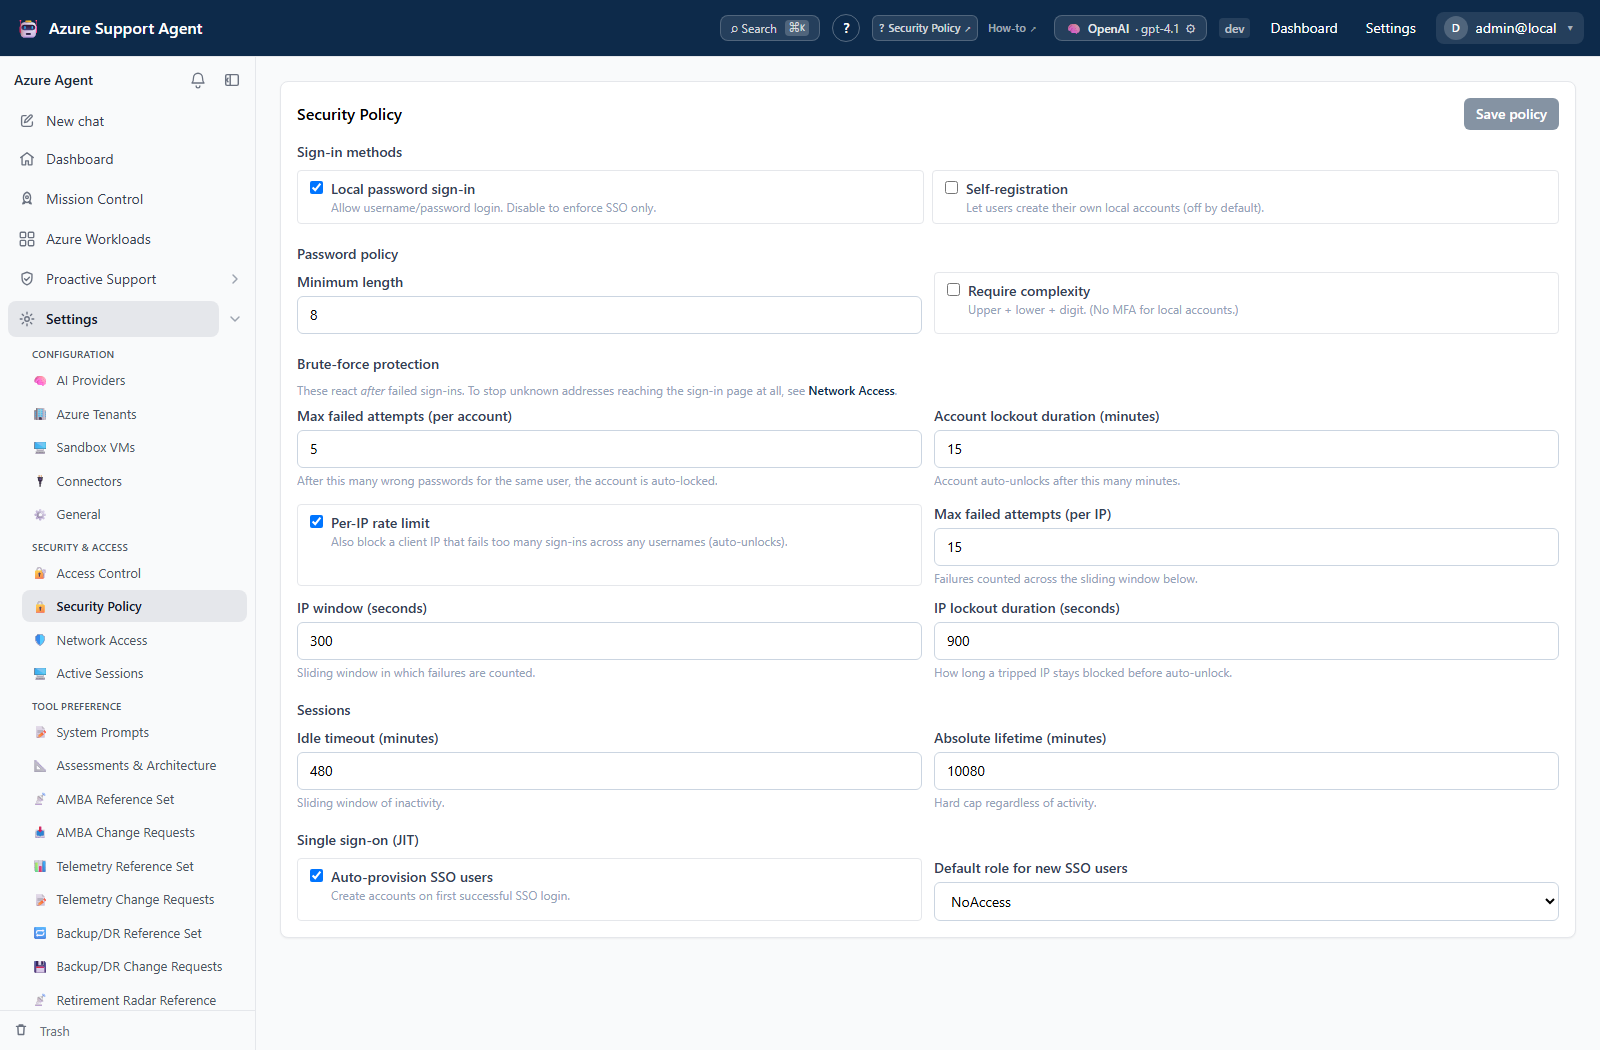
Security Policy — sign-in, lockout, session, and provisioning controls
Security Policy — sign-in, lockout, session, and provisioning controls. The local policy screen separates password sign-in, failed-attempt handling, session lifetimes, and the default role for new SSO users. It is one configuration layer, not an Azure permission or write-approval screen. Displayed defaults are illustrative, not a recommended production baseline; no setting was changed and no enforcement test was performed. Synthetic example data; names, identifiers and measurements do not describe a live tenant. View full-size screenshot.

Guides

Procedures

Task Recipe
Create users, roles, and groups, and connect an SSO provider Manage users, roles, groups, and SSO
Set password, lockout, and session policy, and revoke a session Set policy and revoke sessions
Restrict which IP addresses can reach the application Restrict network access by IP
Store and rotate Azure and provider credentials Manage Azure tenants
Review privileged actions and export them to a SIEM Review usage and audit history

See the permissions reference for the capability keys behind every gate.

Use no real secrets or identifiers in examples. Report product vulnerabilities through the repository’s security process rather than a public issue.


Table of contents


Back to top

Azure Support Agent is open source under the MIT License.

This site uses Just the Docs, a documentation theme for Jekyll.