These views combine Azure Resource Manager, Policy Insights, and Microsoft Graph evidence. They are analysis-first: Policy simulation does not deploy, Identity does not rotate credentials, and IAM does not alter assignments. Policy exemption apply/remove is an explicit Azure-write exception; legacy Identity ticket creation writes to its chosen connector.
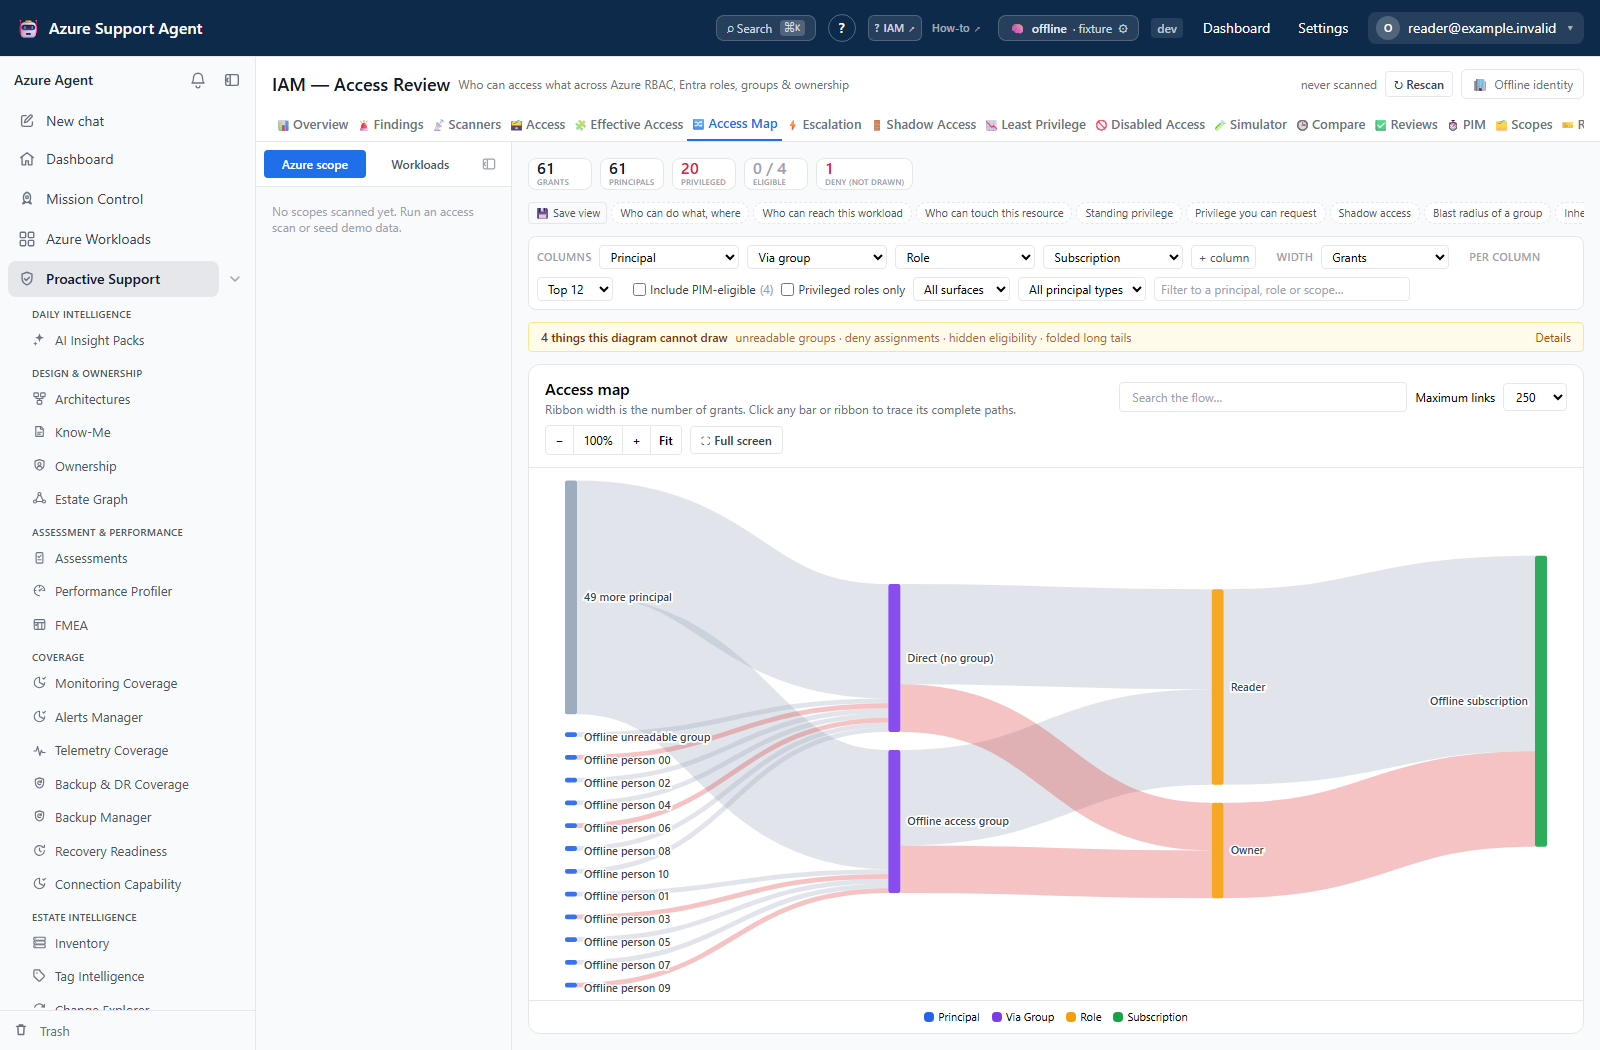
Identity evidence example — distinguish direct and group-derived grant paths. IAM Access Map connects synthetic principals through groups and roles to an offline subscription. Its warning strip preserves unreadable-group, deny, eligibility, and folded-tail limitations. This is a grant-path view, not the action-level Effective Access evaluator, an Azure Policy result, or evidence that a tenant was scanned or remediated. Synthetic example data; names, identifiers and measurements do not describe a live tenant. View full-size screenshot.
Correlate one identity’s cached access and findings, inspect an explicit warning when an account is disabled, request audited activity, and export provenance.